Category AWS

API Gateway Caching

Caching in Amazon API Gateway looks like an easy thing to configure while the outcome is huge: responses get faster, the bill gets smaller, TTL is configured and you didn’t touch a single line of application code. There’s a catch,…
AWS API Gateway throttling vs WAF rate-based rules

API Gateway throttling vs WAF rate limiting: if API Gateway already throttles requests, why would we add rate limiting in AWS WAF too? It looks like the same feature configured twice. You can use both since they actually protect against…

AWS SQS short polling, long polling and Lambda batching

It is widely known that Simple Queue Service, or SQS, is commonly used to decouple applications and processes tasks asynchronously. This means we usually have data producer then SQS and then data consumer. Producer sends messages to SQS queue, while…

AWS Data Ingestion layer

Data ingestion layer is the entry point of a data platform. That means it receives data from external providers, devices, applications or even internal systems and brings it into the platform in controlled way. In AWS ecosystem this layer is…

AWS Fan-out simplified

One of the most common pattern being used within distributed systems on AWS is fan-out. Simple definition for fan-out would be when one event happens multiple independent systems need to react to it. Simple example could be when a user…

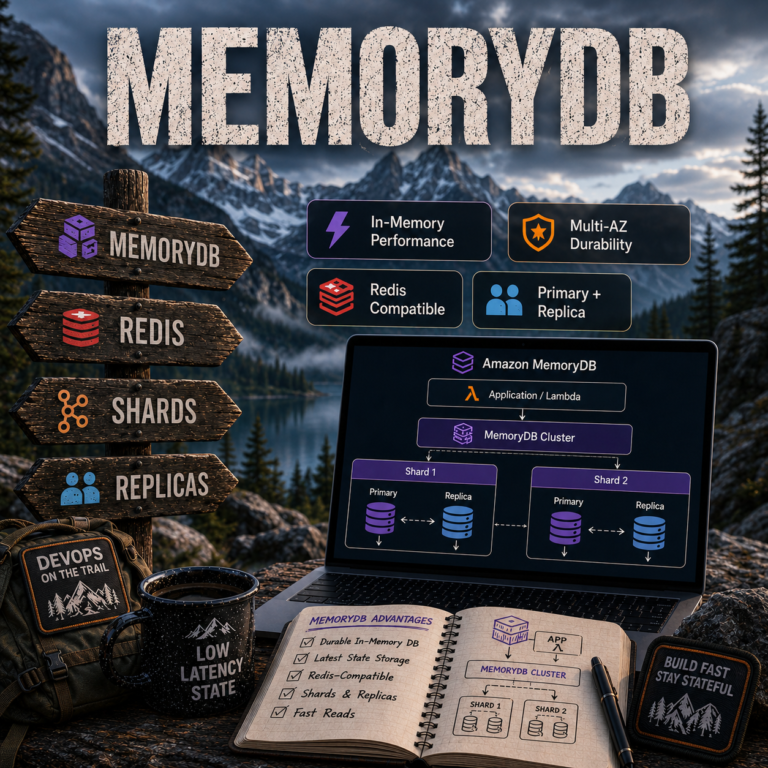
Amazon MemoryDB simplified

When you need very low latency data access, Redis is usually one of the first storage that comes to mind. However traditional Redis is often used as a cache, which means the source of truth still lives somewhere else. Amazon…

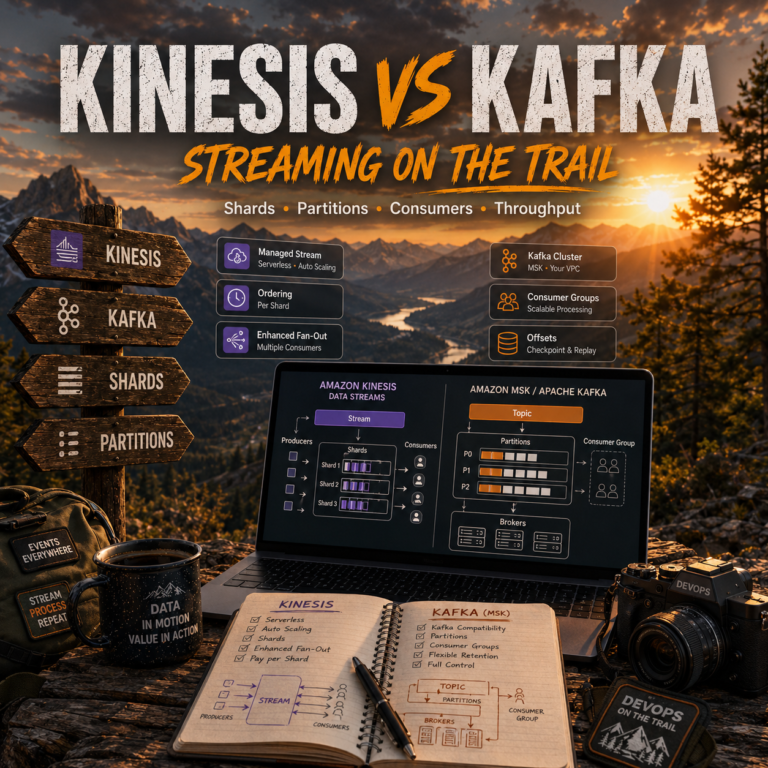
AWS Kinesis Data Stream vs MSK Kafka

When building event-driven architectures and data streaming workloads on AWS, two services often appear in the same conversation: Amazon Kinesis Data Streams and Amazon MSK, which is AWS managed Apache Kafka. At first glance, they solve a similar problem. Producers…

AWS Cognito simplified

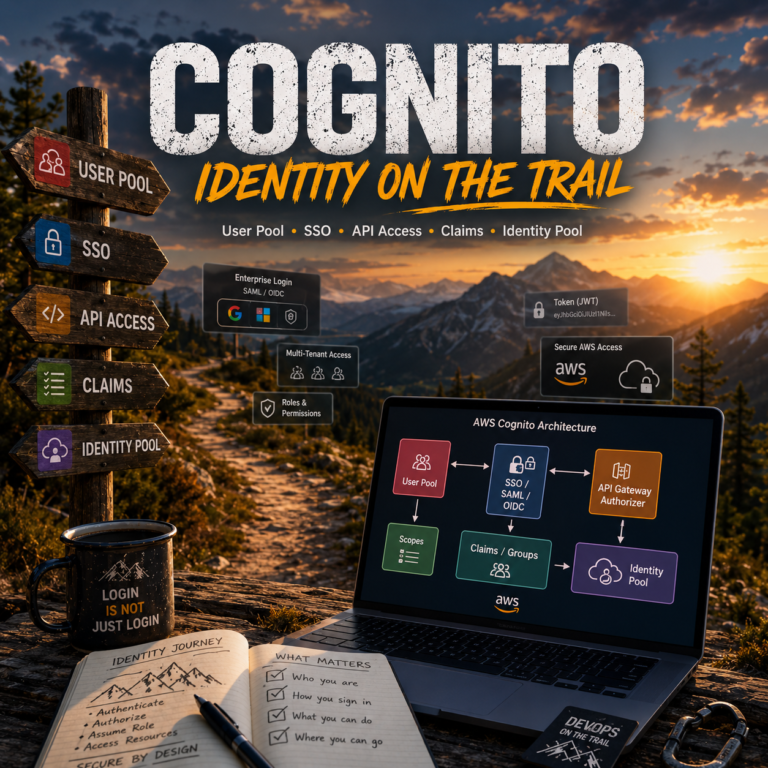
Often when we hear that app would need login, it often sounds as simple feature: a user opens application, enters credentials and gets access. But in real AWS applications, especially enterprise applications, login is usually only the first part of…

GuardDuty Malware Protection for S3 with Terraform

User-uploaded files are a common security risk. If an application allows users to upload PDFs, images, or any documents into S3, those files should be scanned before they are trusted by downstream services. Instead of building a custom pipeline with…